PHP2Shell news 2026: Learn about critical PHP vulnerabilities, security patches, Cloudflare protection, affected PHP versions, and website security steps.
Thank you for reading this post, don't forget to subscribe!PHP2Shell News 2026: Critical PHP Vulnerabilities Trigger Global Cybersecurity Response
What Is PHP2Shell? A Major PHP Security Story in 2026
A major cybersecurity incident involving PHP has prompted an international response from software developers, security researchers, and internet infrastructure providers.
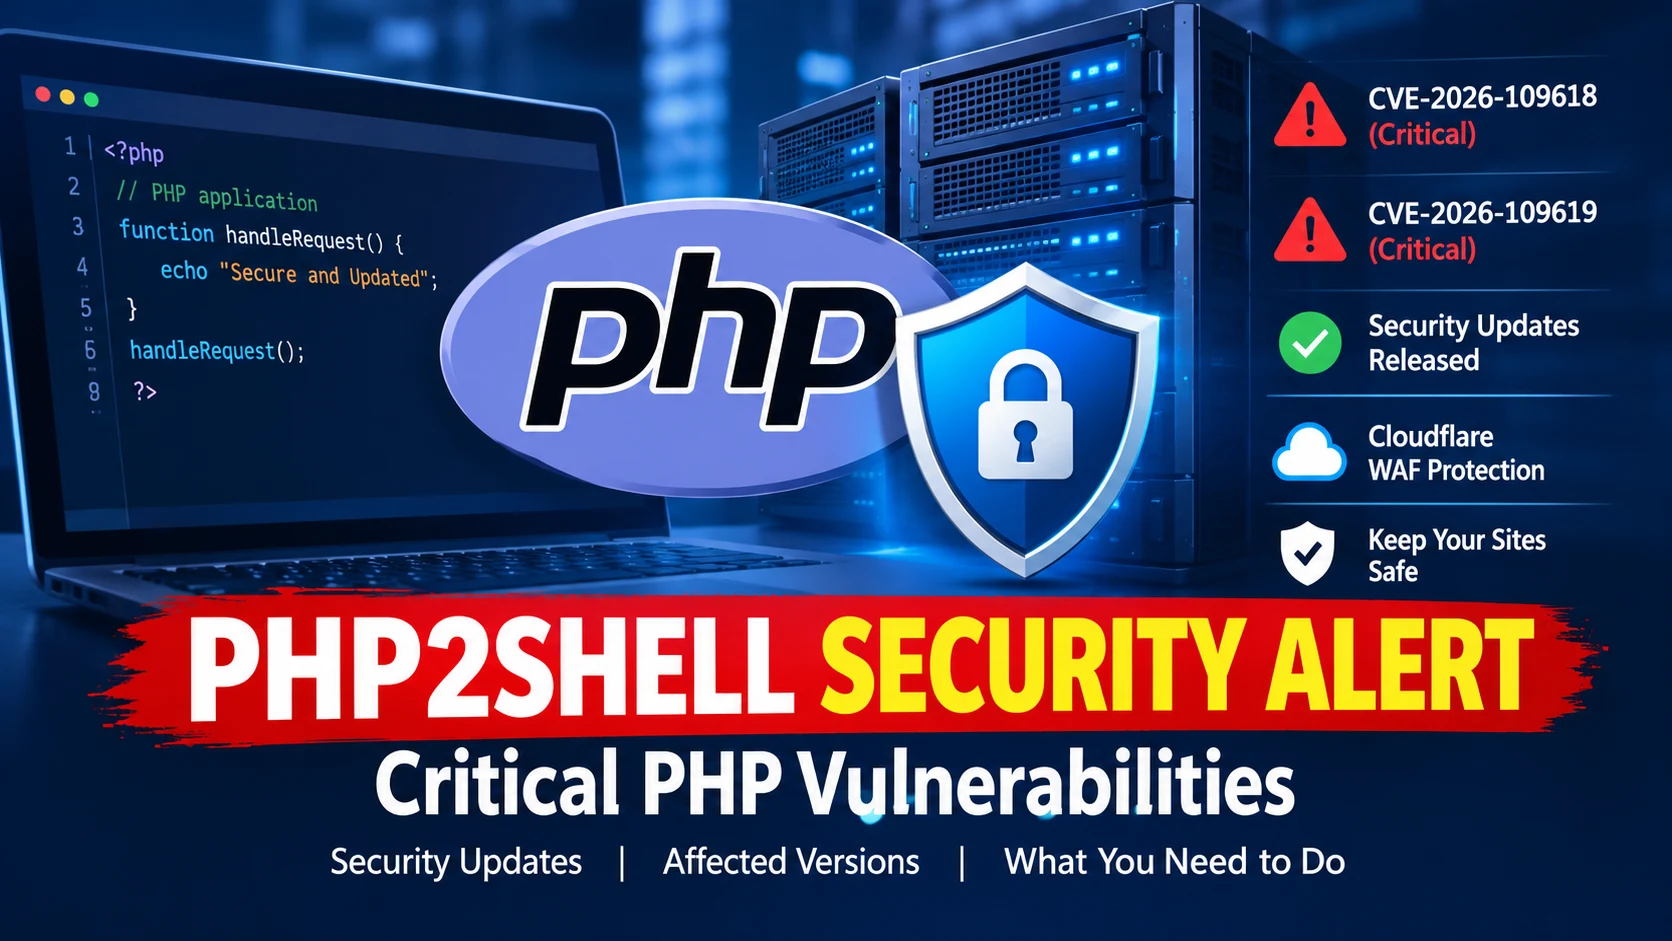
On October 21, 2026, the PHP development team released emergency security updates addressing two critical vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619. Researchers have referred to the vulnerabilities collectively as PHP2Shell.
According to the official PHP announcement, the flaws could allow unauthenticated remote code execution under affected conditions. This means an attacker could potentially execute malicious code on a vulnerable server without first logging in.
The disclosure has attracted attention because PHP powers a wide range of websites and web applications. Organizations running vulnerable installations have been urged to install the appropriate security updates immediately.
Cloudflare has also published details about protections deployed through its web application firewall, while cybersecurity organizations have issued guidance to help administrators assess their exposure.
Why Are the PHP2Shell Vulnerabilities Dangerous?
The PHP2Shell incident involves two separate vulnerabilities in the PHP runtime.
CVE-2026-109618: Remote Code Execution Risk
The first vulnerability relates to PHP’s handling of out-of-memory conditions. Under certain circumstances, an interruption during memory allocation can leave internal request data partially initialized.
If the affected code subsequently processes that invalid state, an attacker may be able to trigger remote code execution.
CVE-2026-109619: Internal State Corruption
The second vulnerability involves stale internal state that may reference request memory after it has been released.
Under particular conditions, the resulting memory-management error can also be exploited to execute code on an affected server.
Both vulnerabilities received a CVSS 4.0 severity score of 9.2, placing them in the Critical category.
These issues affect the PHP runtime itself rather than necessarily being caused by a particular WordPress plugin or website theme.
PHP Security Updates: Which Versions Should You Install?
The PHP development team released the following patched versions on October 21, 2026.
| PHP Branch | Security-Fixed Version |
|---|---|
| PHP 8.5 | 8.5.12 |
| PHP 8.4 | 8.4.27 |
| PHP 8.3 | 8.3.36 |
| PHP 8.2 | 8.2.35 |
The official PHP announcement states that updating is the appropriate way to address these vulnerabilities; there is no complete mitigation that replaces installing the fixes.
Website owners should verify their installed PHP version and use the correct package supplied by their hosting provider or operating-system vendor.
Older, unsupported PHP versions may require migration to a supported release or guidance from a vendor that provides extended security maintenance.
Cloudflare Deploys Protection Against PHP2Shell
Cloudflare has reported deploying web application firewall protections for the newly disclosed PHP vulnerabilities.
According to the company’s October 21, 2026, security blog post, Cloudflare deployed protections for customers using its free or paid WAF before public disclosure of the vulnerabilities.
A web application firewall can help detect or block malicious requests before they reach a vulnerable application. However, WAF protection should not be treated as a replacement for updating the underlying PHP software.
Website owners should check their security provider’s specific guidance rather than assuming that every server, hosting environment, or third-party firewall has the same protection.
How Is the Cybersecurity Community Responding?
The PHP2Shell incident has prompted coordinated activity among software maintainers, researchers, and security organizations.
- PHP development team: Released security updates and published technical details about the vulnerabilities.
- Cloudflare: Reported deploying WAF protections ahead of public disclosure.
- Wiz Research: Published an explanation of the vulnerabilities and their potential impact.
- UK National Cyber Security Centre: Advised organizations to identify affected PHP systems, monitor for suspicious activity, and apply updates.
- Other security teams: Published technical assessments and remediation recommendations to help organizations prioritize their response.
The incident demonstrates why coordinated vulnerability disclosure matters. Security researchers, software maintainers, and infrastructure providers can work together to reduce exposure while patches and defensive measures are prepared.
Are WordPress Websites Affected by PHP2Shell?
WordPress is built primarily with PHP, so the PHP2Shell incident is relevant to WordPress hosting environments running affected PHP versions.
However, that does not mean every WordPress website has been compromised or that every installation is equally exposed.
Website owners should:
- Check the PHP version used by their hosting account.
- Contact their hosting provider if they cannot update PHP themselves.
- Install the appropriate fixed PHP release.
- Keep WordPress core, themes, and plugins updated.
- Review server logs for suspicious activity.
- Use a properly configured firewall and maintain verified backups.
- Investigate possible compromise if there are signs of unauthorized code execution.
Updating WordPress plugins alone does not fix a vulnerability in the underlying PHP runtime. The PHP installation itself must also be addressed.
How to Check Your PHP Version
Website owners can usually check their PHP version through their hosting control panel.
For example, in cPanel, look for the PHP version management tool. The name and location vary between hosting providers.
Developers with command-line access can run:
php -v
This displays the PHP version used by the command-line executable. Note that a website may use a different PHP version through PHP-FPM, Apache, or another hosting configuration, so confirm the version serving actual web requests.
Avoid publishing a publicly accessible phpinfo() page to check the version. Such pages can reveal sensitive server configuration details.
What Should Website Administrators Do Next?
The immediate priority is to identify affected systems and apply the appropriate security fixes.
Organizations should inventory their PHP installations, prioritize public-facing servers, verify that patches have been applied, and monitor for signs of exploitation.
If updating is not immediately possible, follow the recommendations of the relevant security authority or hosting vendor. Where a vulnerable system cannot be adequately protected, temporarily isolating it may be necessary.
Conclusion
PHP2Shell has become an important cybersecurity story because it highlights the risks associated with vulnerabilities in widely deployed server-side software.
The PHP development team has released fixes for CVE-2026-109618 and CVE-2026-109619, and Cloudflare has reported deploying additional WAF protections. Cybersecurity organizations have also issued guidance to help administrators respond.
For website owners, the practical message is clear: verify your PHP version, install the appropriate security update, review your security controls, and investigate any signs of suspicious activity.
For the latest technical instructions, always consult the official PHP security advisory and your hosting provider’s guidance.
PHP2Shell has prompted urgent security updates after two critical PHP vulnerabilities were disclosed. Discover the affected versions, Cloudflare’s WAF response, and steps website owners should take to protect their servers.
Heading Structure
H1: PHP2Shell News 2026: Critical PHP Vulnerabilities Trigger Global Cybersecurity Response
H2: What Is PHP2Shell? A Major PHP Security Story in 2026
H2: Why Are the PHP2Shell Vulnerabilities Dangerous?
H3: CVE-2026-109618: Remote Code Execution Risk
H3: CVE-2026-109619: Internal State Corruption
H2: PHP Security Updates: Which Versions Should You Install?
H2: Cloudflare Deploys Protection Against PHP2Shell
H2: How Is the Cybersecurity Community Responding?
H2: Are WordPress Websites Affected by PHP2Shell?
H2: How to Check Your PHP Version
H2: What Should Website Administrators Do Next?
H2: Conclusion
1. Official PHP Security Announcement
The primary source for the affected vulnerabilities and released PHP versions.
https://www.php.net/archive/2026.php
2. Cloudflare Security Blog
Details of the WAF protections deployed for PHP2Shell.
https://blog.cloudflare.com/php-vulnerabilities-waf-protection
3. Wiz Research
Technical explanation of PHP2Shell and the vulnerabilities discovered by security researchers.
https://www.wiz.io/blog/php2shell-php-rce
4. UK National Cyber Security Centre
Official security guidance for organizations running PHP.
https://www.ncsc.gov.uk/news/critical-security-issue-affecting-php
5. OpenAI — Coordinated Vulnerability Disclosure
Background on the coordinated response involving PHP vulnerabilities and security researchers.
https://openai.com/index/coordinated-disclosure-of-critical-vulnerabilities
6. Reuters
Independent reporting on the impact of the PHP vulnerabilities and the response from website operators.
Editorial note: This article is an original English-language summary based on the linked sources, not a verbatim reproduction. Recheck the official PHP advisory immediately before publication because security guidance can change.